


Bot attacks and repeated automated requests can consume resources that your WooCommerce store needs for real shoppers. Review traffic patterns and server measurements before choosing a mitigation or upgrading hosting.
In 2026, AI-driven bots generate 52% of global traffic and up to 70% of dynamic resource usage. This creates a massive resource crisis for shared and even managed WordPress hosting. Every time a bot hits a WooCommerce page, it triggers a database query. While a human might read a page for two minutes, a bot can hit 50 pages in two seconds.
The Core Values: The Cost of Automated Traffic
To understand the impact, let’s look at the raw data from leading 2025-2026 industry reports:
- Resource Hijacking: Malicious bots are responsible for up to 70% of dynamic resource consumption (CPU and RAM) on web servers.
- Infrastructure Burn: Large eCommerce platforms, such as KaBuM!, have found that up to one-third of their entire infrastructure capacity was being consumed solely by malicious bot traffic.
- Financial Drain: Bad bot attacks are costing businesses up to $116 billion every year.
- Conversion Killers: Every one-second page delay caused by bot-induced server lag can drop your conversion rates by 7%.
Phase 1: The “Noisy Neighbor” and Server CPU Locking
One of the most misunderstood parts of WooCommerce speed is how bot traffic affects your underlying server. If you are on shared or VPS hosting, you are susceptible to the “Noisy Neighbor” effect.
When an AI crawler or a malicious scraper hits a server, it consumes a slice of processing power. If five sites on that same server are being crawled simultaneously by an aggressive bot (like Meta’s or OpenAI’s), the CPU usage hits a ceiling. The 2026 AI Bot Impact Report highlights that AI crawlers quadrupled their traffic share in just eight months, with OpenAI’s GPTBot alone growing by 305%.
Case Value: A typical bot attack can generate 11 billion requests from residential proxy networks in just seven days. For a small store, this isn’t just “traffic” it is a Denial of Service. When your RAM is exhausted by these requests, the server swaps memory to the disk, which drastically slows down performance for every real human visitor.
Phase 2: Core Web Vitals and SEO Decay
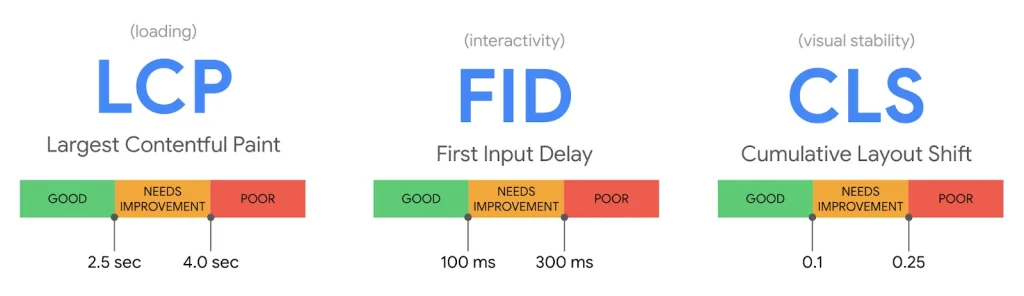
Google’s 2026 algorithm is ruthless regarding Interaction to Next Paint (INP). If your server is busy serving 1.7 billion requests from OpenAI crawlers (as seen in recent DataDome logs), your human users will experience lag.
- LCP (Largest Contentful Paint): Bot-induced server lag causes your “Time to First Byte” (TTFB) to skyrocket, which pushes your LCP out of the “Good” range.
- INP (Interaction to Next Paint): If the server is locked up processing bot-driven database queries, it cannot respond to a human clicking “Add to Cart.” This creates a poor INP score, signaling to Google that your site is low-quality.
- Crawl Budget Depletion: Search engines assign a “crawl budget” to your site. If aggressive AI scrapers consume your server’s bandwidth and connection limits, Googlebot may interpret the slow response as a sign of poor quality and crawl your site less frequently.
Phase 3: The 2025-2026 Bot Surge Reports
We are currently seeing a “Seismic Shift” in bot complexity. Legacy defenses are collapsing as AI-driven traffic reshapes the web.
1. DataDome: The Holiday Surge
In December 2025, AI-driven bot attacks surged by 135% year-over-year. DataDome’s research shows that while Black Friday and Cyber Monday were busy, the bot activity reached “unprecedented heights” throughout the month, with some luxury retail brands seeing over 27 million scalping requests in 30 days.
2. Cloudflare: The DDoS Explosion
Cloudflare’s 2025 data shows an explosion in AI crawlers and DDoS attacks. In the third quarter of 2025 alone, they mitigated 8.3 million DDoS attacks—an average of 3,780 attacks per hour. The “Aisuru” botnet unleashed hyper-volumetric attacks routinely exceeding 1 terabit per second.
3. Imperva & Akamai: The API and Commerce Threat
Imperva’s 2025 Bad Bot Report notes that bad bots now account for 37% of all internet traffic. Akamai reported that the Commerce industry has the most AI bot activity of any sector, reaching more than 25 billion bot requests in just a two-month observation period.
Phase 4: Why “robots.txt” is No Longer a Defense
Many store owners think that adding “Disallow” to their robots.txt file will save them. Honestly, it’s like putting a “Please Don’t Enter” sign on a door without a lock.
The 2025 Global Bot Security Report revealed that 88.9% of domains disallow GPTBot in their robots.txt, yet AI-powered crawlers often ignore these directives. Static blocking strategies are obsolete. Only 2.8% of 16,900+ domains tested were fully protected against the threats vectors analyzed in 2025.
Phase 5: Mitigation and The Swift Commerce Solution
The goal of bot mitigation is to move from a reactive posture to a proactive one.
When we built the security features into Swift Commerce, we prioritized “Invisible Defense”. You cannot afford to slow down your human customers with old-fashioned CAPTCHAs that ask them to find motorcycles in a grid of photos.
1. Invisible reCAPTCHA v3 Integration
By using Google reCAPTCHA v3, Swift Commerce helps you identify bot behavior without frustrating your users. It assigns a score to every interaction, allowing the server to drop connections from suspicious bots before they hit your database.
Value: Organizations that successfully block aggressive AI crawlers have seen a 75% reduction in traffic and significant savings on server costs.
2. Email Verification for User Integrity
Bot operators use “fake account creation” to fuel fraud and scrape proprietary data. In December 2025, over 595k fake account creation requests were detected against a single financial service business.
Swift Commerce’s Email Verification ensures that only verified human users can register, effectively cutting off “Ghost Users” from your database.
3. Behavioral Analysis (Coming in the 2026 Roadmap)
Because bots are becoming “advanced and persistent” meaning they simulate complete browsers and human activity mitigation requires analyzing behavioral signals. By consolidating your features (Wishlists, Bundles, Recovery) into a single addon/plugin, Swift Commerce reduces the “attack surface” of your store, making it easier to monitor and protect.
Reference Links & Authentic Organizations
This case study is grounded in data provided by the world’s leading security and infrastructure organizations:
- Imperva (Thales): 2025 Bad Bot Report
- DataDome: 2025 Global Bot Security Report
- Cloudflare: 2025 Q3 DDoS Threat Report
- Akamai: State of the Internet Security Report 2025
- F5 Labs: 2025 Advanced Persistent Bots Report
Final Summary: Performance as Security
In 2026, you cannot separate site speed from security. If your store is being feasted upon by 1.7 billion bot requests, no amount of “speed optimization” will save your conversion rates.
By implementing a Zero-Bloat architecture and native security features like invisible reCAPTCHA, you aren’t just “protecting” your site, you are reclaiming your server resources for the people who actually pay the bills: your customers.